
Power BI Security and Governance: Permissions, RLS, and Labels
Introduction
Power BI security starts with three separate decisions. Who can open the report? Which rows can they see? How will a supported export be protected? A regional director might open a shared sales report, see only their own region, and receive an Excel export that retains its Confidential label. Those outcomes come from different controls.
This lesson covers the security and governance objectives in Manage and secure Power BI (15–20% of the April 20, 2026 PL-300 outline). You will configure item and semantic model permissions, implement and test row-level security (RLS), assign role members, and apply sensitivity labels.
Learning objectives
- Explain the security layers: workspace roles, item permissions, app audiences, semantic model permissions, RLS and sensitivity labels.
- Grant and revoke Read, Reshare, Write and Build permissions on items.
- Create static RLS roles and dynamic RLS with
USERPRINCIPALNAME(). - Validate roles with View as and assign members in the service.
- Explain what RLS does not cover and when object-level security applies.
- Apply sensitivity labels and describe their effect on exports.
1. Security layers: who controls what
Identify the item, the data, and the people who need access. Then select a control for each part of that decision.
| Layer | Question it answers | Where configured |
|---|---|---|
| Workspace role | Who can see or edit everything in this workspace? | Workspace > Manage access |
| Item permissions | Who can open, reshare, edit or build on this specific report or model? | Item > Manage permissions |
| App audience | Which curated content does this consumer see? | Workspace > App > Audiences |
| Semantic model permission | Who can connect to this model to build new content? | Model > Manage permissions (Build) |
| Row-level security | Which rows of data does this viewer see? | Desktop (roles) + service (members) |
| Sensitivity label | How must the exported or shared file be protected? | Item settings or Desktop (Microsoft Purview Information Protection) |
Principle: grant the least privilege, use groups instead of individuals, and review workspace roles and app audiences to decide how people should receive the content.
2. Item-level access and semantic model access
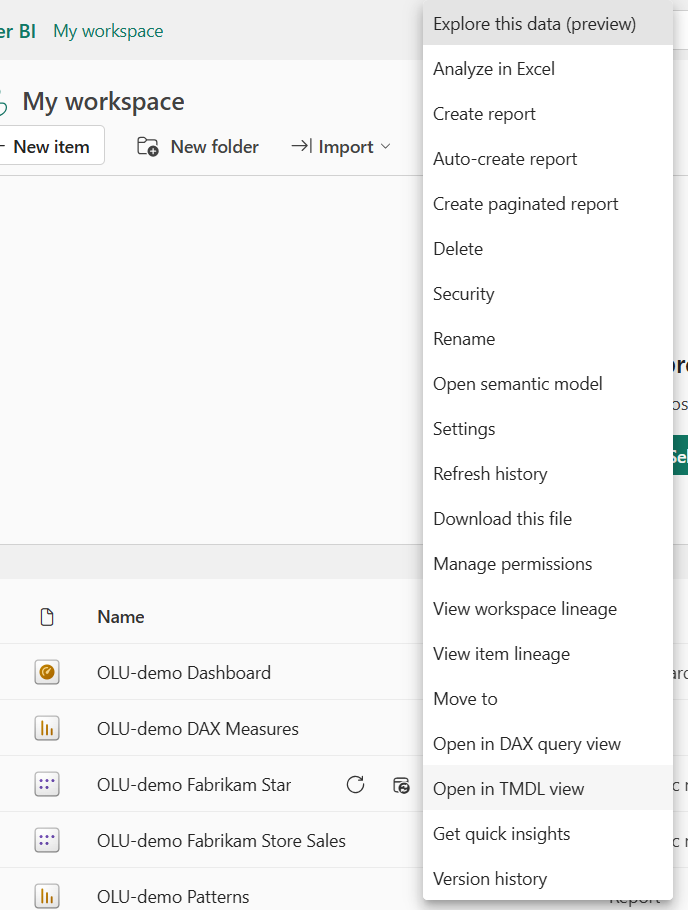
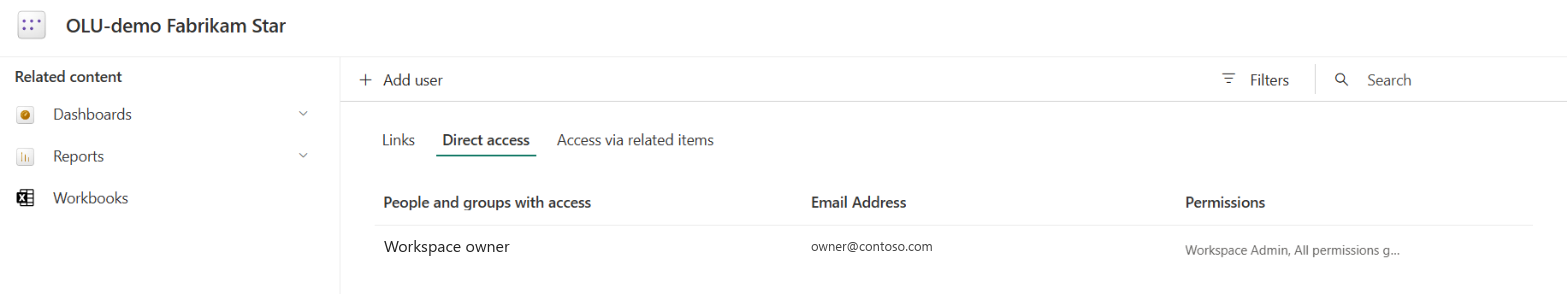
You can grant access to a single item without making someone a workspace member. From the item's ellipsis menu choose Manage permissions. The permissions to know:
| Permission | Allows |
|---|---|
| Read | Open a report or dashboard, or use the semantic model through existing content |
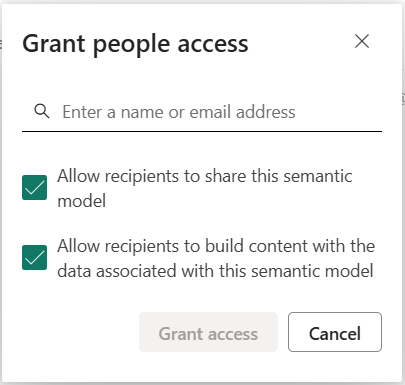
| Reshare | Share the item with others (granted when sharing with "Allow recipients to share") |
| Write | Edit or republish the semantic model, inherited by Contributors and higher workspace roles |
| Build | Build new content on a semantic model: connect from Desktop, Analyze in Excel, create new reports in the service, export underlying data |
Semantic model access
Treat the semantic model as the data access boundary. Read and Build both allow access to data within the permissions and security roles in effect.
- Consumers need Read access to the report and its underlying model. Grant Build separately or use the share dialog’s Build option for users who need to create content. Review any existing grants before concluding that a user has read-only access.
- To let analysts create new reports on a shared, certified model, grant Build on that model, ideally through a security group. Without Build, Get data > Power BI semantic models does not list the model for them.
- Removing a user from a workspace also removes the permissions inherited from the role, but direct item permissions remain until revoked. Always audit both lists.
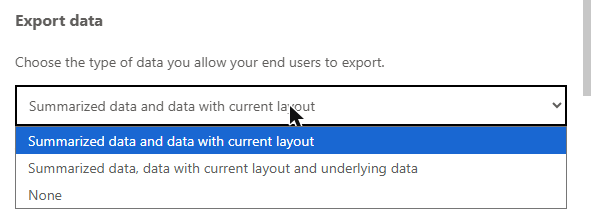
- Analyze in Excel and export of underlying data generally require Build for consumers. Export of summarized data can be available without Build. Tenant settings, report settings, and the type of visual also affect export.
Pitfall: sharing a report link with "Anyone in the organization with the link" does not mean RLS is bypassed; RLS still filters consumers who lack Write access to the model. But if a recipient also has an editing role in the workspace that owns the model, RLS does not apply to them.
Worked example: choose item permissions
Statement. Camille, an analyst in the organization, must (1) open the "Supplier KPIs" report, (2) build her own report on the "Supplier model", (3) never edit the original, nor share it onward.
Reasoning.
- Open the report: Read on the report and the required access to its semantic model. Use a link for specific people and leave Allow recipients to share off.
- Build her own report: Build on the semantic model, granted in the model's Manage permissions.
- Never edit: she must not hold a Contributor, Member or Admin role, so no workspace role is needed at all; Write is not granted.
- Not share: leave Reshare off.
Why not the alternatives. Making her a workspace Contributor grants write access to everything and bypasses RLS. Making her a Viewer exposes every item in the workspace. Giving only Read on the report prevents her from building new content.
3. Row-level security (RLS)
RLS restricts rows a user can see in a semantic model by applying DAX table filter expressions attached to a role. Author roles in Power BI Desktop or in the service model editor where supported. Assign members in the service. RLS applies to users with read-only model access, including Viewers and app consumers. Build permission alone does not bypass RLS. Users with Write access, including Admins, Members, and Contributors of the owning workspace, bypass RLS.
Static RLS
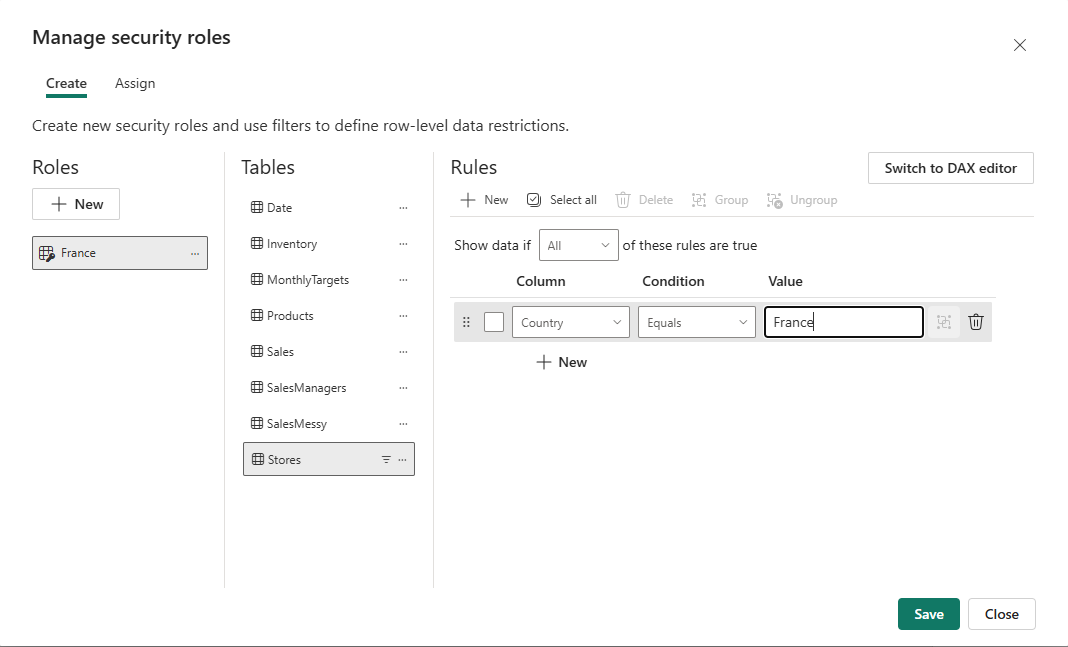
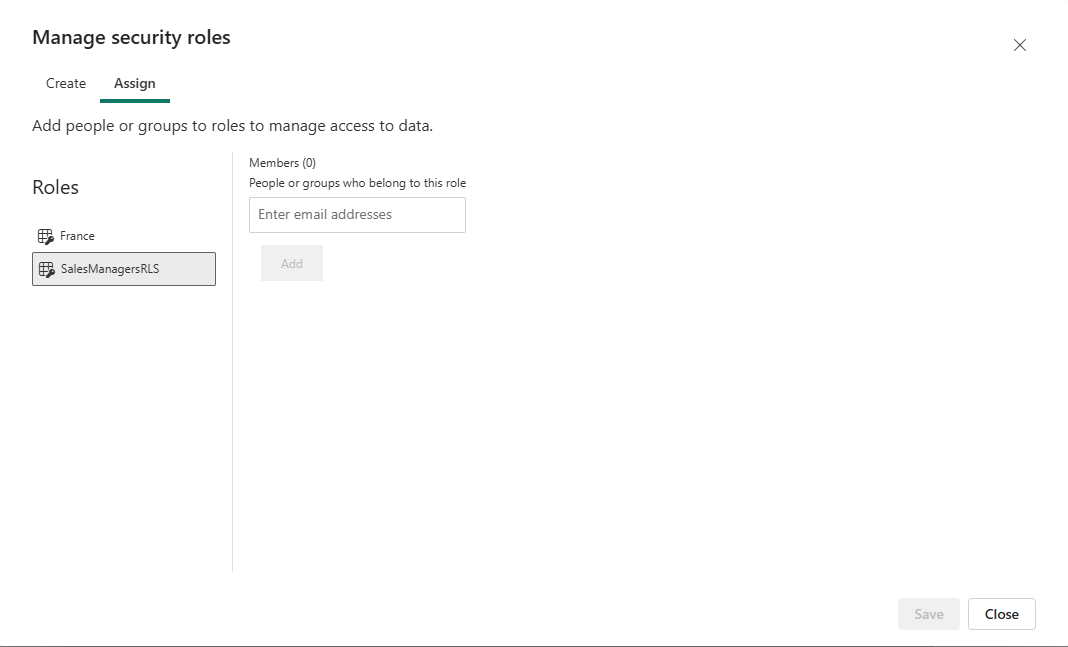
A static role hard-codes the filter. In Desktop: Modeling > Manage roles > Create, name the role, select the table, and enter the filter. In the service, editing the semantic model (Home > Manage roles) opens the same Manage security roles dialog: a rule builder (column, condition, value), a Switch to DAX editor button that shows the equivalent DAX expression, and an Assign tab for members.
-- Role "Europe": rows of the Territory table
[Region] = "Europe"
A user in that role sees the matching Territory rows and the related Sales rows when an active relationship carries the filter from Territory to Sales. Static roles scale poorly: one role per region, each with its members.
Dynamic RLS
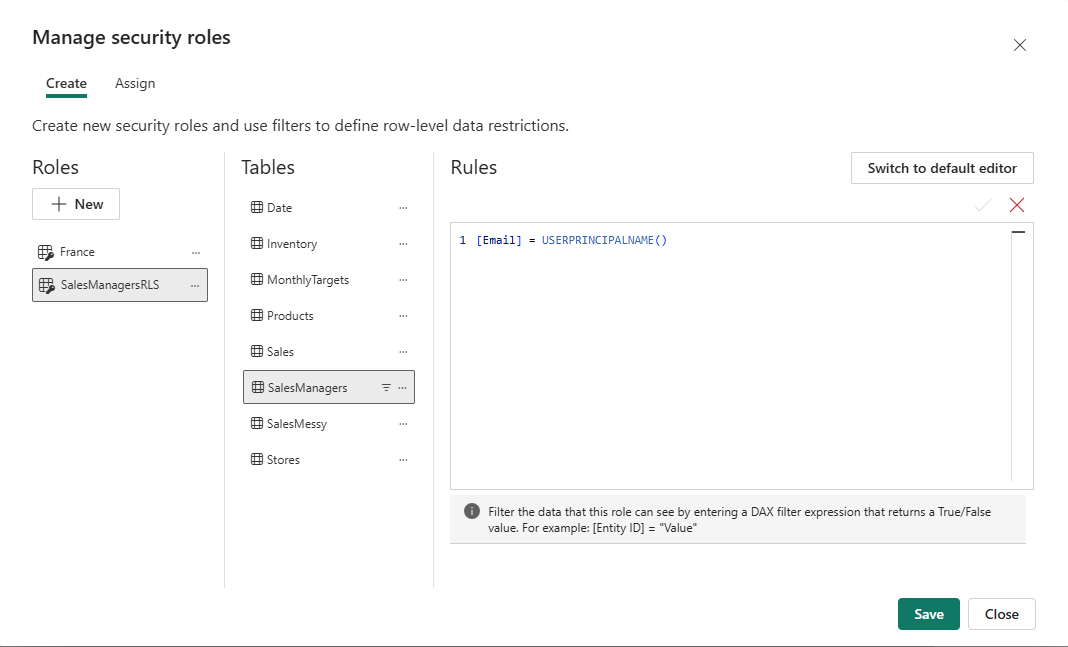
A dynamic role uses the signed-in user's identity and a mapping table, so a single role serves everybody.
-- Role "RegionalManager" on the table UserRegion (columns: UserEmail, Region)
[UserEmail] = USERPRINCIPALNAME()
In this Import model, Territory[Region] is unique. The UserRegion mapping table can have several rows per region. Security must propagate from UserRegion to Territory, then from Territory to the fact table. Key functions:
| Function | Returns | Remark |
|---|---|---|
USERPRINCIPALNAME() |
The user's UPN (e-mail like) | Compare with the actual sign-in UPN, which can differ from the mailbox address |
USERNAME() |
DOMAIN\user in Desktop, the UPN in the service |
Differs between environments; tests can mislead |
USEROBJECTID() |
Entra object ID | Useful when e-mails change |
LOOKUPVALUE() |
Looks up a value in another table | For mapping users to attributes |
Filter direction. In this design, configure the Territory (1) → UserRegion (*) relationship with Both cross-filter direction and Apply security filter in both directions. Keep the Territory (1) → Sales (*) relationship active with filters flowing toward Sales. Scope bidirectional security to the relationship that needs it and test for ambiguous paths. Review Power BI model relationships and filter direction before changing the model.
Testing with View as
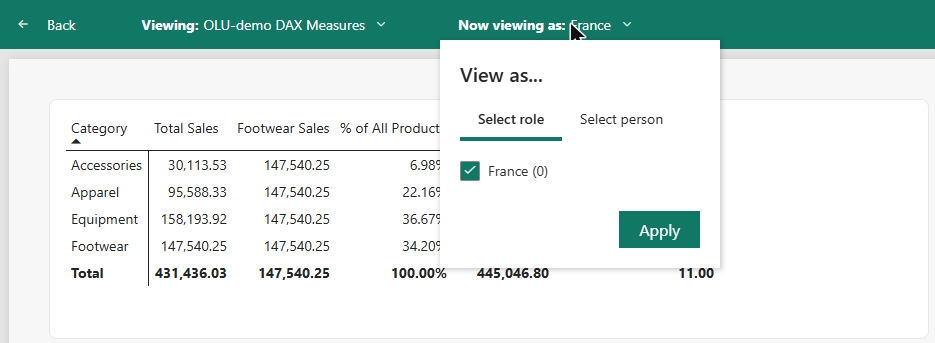
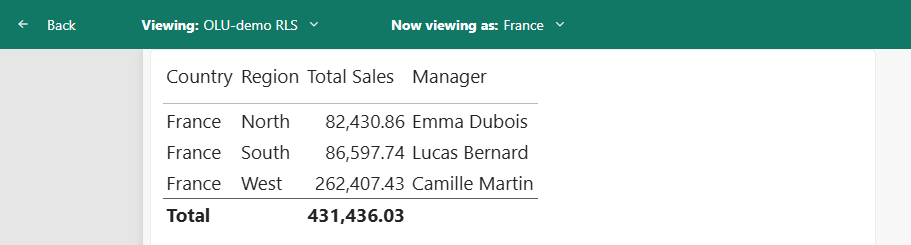
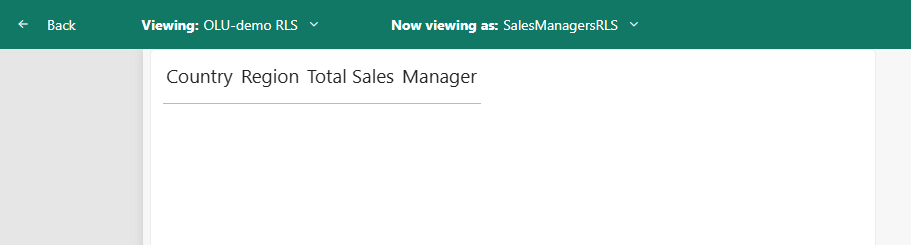
In Desktop, Modeling > View as lets you tick one or more roles (and optionally "Other user" to emulate a UPN) and view the report as that role. In the service, open the model's ellipsis, Security, and use Test as role: the page shows Now viewing as (tick one or more roles, or Select person to emulate a user) and Viewing, which picks any report built on the model. Also open the published report with a real consumer account. Service simulation has limitations, including DirectQuery with single sign-on (SSO), and a guest’s UPN can differ from the address in the mapping table.
Assigning members in the service
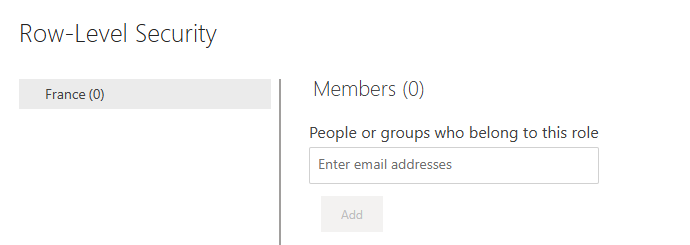
Assign users or supported groups in Semantic model > Security > select the role. Microsoft Entra security groups and supported distribution groups can be used. Microsoft 365 groups are not supported for RLS membership. A user assigned to several RLS roles sees the union of the rows those roles allow. A read-only consumer with no matching role cannot see protected data. The report can show empty results or an access error.
What RLS does not do
- It does not apply to workspace Admin, Member and Contributor.
- It does not hide tables or columns. Hiding a column in the model is not security. Use object-level security (OLS) (configured through TMDL view or a supported external model editor) to secure tables and columns.
- A Power BI semantic model can define RLS in DirectQuery mode. For a live connection to Analysis Services, define roles in the Analysis Services model.
- Roles on a shared semantic model apply to every report built on it.
Worked example: dynamic RLS for sales managers
Statement. Fabrikam has 40 sales managers. Each must see only sales for the regions listed for them in an HR table ManagerRegion(ManagerEmail, Region). New managers are added weekly, and the Import model contains a Territory dimension with one row per region and a Sales fact.
Reasoning.
- One dynamic role, not 40 static roles.
- Relate
ManagerRegion[Region]to the uniqueTerritory[Region]. Apply the bidirectional security setting on the mapping relationship and verify that the active Territory-to-Sales relationship carries the filter to the fact. - Define the role "ManagersRLS" with the filter on
ManagerRegion:[ManagerEmail] = USERPRINCIPALNAME(). - Test with View as > Other user using a manager’s UPN. Check a manager with two regions and one with no matching mapping row.
- Publish, then in the service assign the security group Sales-Managers to the role. Add new managers to the group and the HR table, then refresh the imported mapping before verifying their access.
- Give managers Viewer access or share through an app. Verify that none inherits Write on the model through another group.
Why not the alternatives. Hiding the fact table columns does not filter rows. Static roles require maintaining separate membership lists. Adding a new region or changing a role rule also requires a model change. Setting the filter on Sales directly with a hardcoded email list becomes unmaintainable.
4. Sensitivity labels
Sensitivity labels from Microsoft Purview Information Protection classify and protect content (for example Public, Internal, Confidential, Highly Confidential). They require that the tenant admin enables labels for Power BI and that users are in the label policy. Facts to know:
- Labels can be applied to semantic models, reports, dashboards, dataflows in the service, and to .pbix files in Desktop.
- A label does not change who can open the item inside Power BI; access is still decided by workspace roles, permissions and RLS. Its value is in protecting data when it leaves: supported export paths can carry the label and, when configured, encryption. For example, supported Excel exports carry protection. CSV and PowerPoint’s live-data export do not carry the label.
- Downstream inheritance: when a report is built on a labeled semantic model, the label can propagate; the tenant setting controls inheritance and mandatory labeling.
- A mandatory label policy can require a label when users create or edit covered items. Whether users must choose it manually depends on defaults and the item workflow.
- Users can downgrade a label only if the policy allows it, usually with a justification.
- Labels can be applied automatically by the admin through default labels.
| Need | Right tool |
|---|---|
| Hide rows from a user | RLS |
| Hide a column or table | Object-level security |
| Keep the Excel export classified and encrypted | Sensitivity label with protection |
| Let an analyst build on a model | Build permission |
| Show a certified badge | Endorsement |
Worked example: protect a confidential report
Statement. HR publishes a report on salary bands. The data may be seen by HR only. Exports must stay protected when saved to a laptop.
Solution.
- Put the report in an HR-only workspace; grant HR groups the Viewer role or give an HR app.
- Apply the Confidential – HR sensitivity label (with encryption for HR only) to the semantic model and the report.
- Create an RLS role if HR business partners may see only their own units.
- Disable export or "Publish to web" where governance requires it.
Why not the alternatives. A label alone does not stop a user with workspace access from reading the report. RLS alone does not protect a file once exported. Hiding the report in an app navigation is not a security control.
5. Governance practices that the exam expects
- Use security groups for roles, audiences, RLS membership and Build permission.
- Separate development and production workspaces and promote through deployment pipelines.
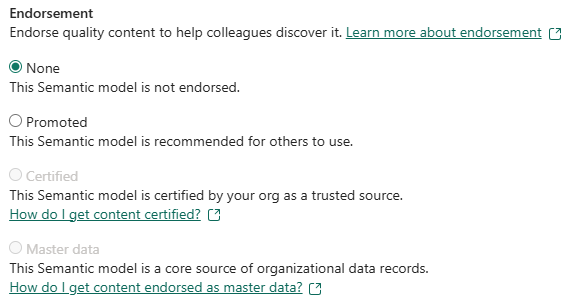
- Endorse trusted models (promote, certify) and educate users to reuse them.
- Review who has access regularly from Manage access and Manage permissions.
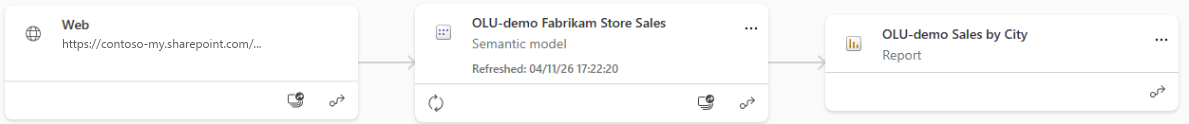
- Use lineage and impact analysis before changing shared models.
- Limit Publish to web, export and sharing with tenant settings handled by the Power BI administrator.
6. Pitfalls and exam tips
- RLS = rows, OLS = tables and columns. Hiding a column is not security.
- Define RLS roles in Desktop or a supported service model editor. Assign users to the roles in the service.
- Check with a consumer account. The author’s normal report view bypasses RLS when the author has Write access. Use View as to inspect the role, then confirm behavior as a real reader.
USERPRINCIPALNAME()is the recommended function for dynamic RLS in the service.- A reader without a matching role cannot see RLS-protected data. A reader in several roles sees the union of their allowed rows.
- Build permission is what enables building on a shared model and Analyze in Excel.
- Sensitivity labels protect content on export; they do not grant or deny access in the service.
- Do not confuse sharing (item permissions), apps (audiences) and workspace roles.
7. Mini case study
Situation. Adventure Works shares a "Global Sales" semantic model. Requirements: (1) regional directors see only their region; (2) the same model is certified and reused by 12 report authors in other workspaces; (3) a monthly Excel export of the report goes to the board and must remain classified Confidential; (4) the BI team needs to edit the model; (5) a contractor must read a single report only.
Questions. Design the security.
Solution (commented).
- Regional directors. A dynamic RLS role using a
DirectorRegionmapping table andUSERPRINCIPALNAME(). Assign the group Regional-Directors in the service. Give them Viewer or an app only. - Reuse. Certify the model through an authorized certifier and grant Build to the group Report-Authors. They do not need workspace membership.
- Board export. Apply the Confidential label to the model and report so that exported Excel files inherit it.
- BI team. Give the BI team Contributor and the lead Member if the lead publishes the app. Use View as and a separate consumer account to verify RLS.
- Contractor. Share the report with Read and provide the required model access. Withhold Reshare and Build. If the contractor must see only a data subset, assign and test the appropriate RLS role.
Common wrong answers. Giving directors Contributor "so that they can explore" (RLS disappears); hiding columns to protect rows; building 12 static roles; applying a label and believing it blocks access; using Publish to web for the contractor.
Key terms
- Item permission: right on a single item (Read, Reshare, Write, Build).
- Build permission: right to create content on a semantic model.
- Row-level security (RLS): DAX-based row filter attached to a role.
- Static / dynamic RLS: fixed filter versus filter based on the signed-in user.
- USERPRINCIPALNAME(): DAX function returning the user's UPN.
- View as: Desktop and service feature to test roles.
- Object-level security (OLS): hides tables or columns from roles.
- Sensitivity label: Purview classification and protection applied to content.
- Least privilege: grant only what is needed.
Summary checklist
- I can list the security layers and what each one decides.
- I can grant Read, Reshare, Write and Build and know when each applies.
- I can write a static and a dynamic RLS filter and test it with View as.
- I know where to author model roles and assign their members.
- I know RLS does not apply to Admin, Member and Contributor and does not hide columns.
- I can explain what sensitivity labels do on export and what they do not do.
- I can design a least-privilege setup with security groups.
Official sources
- Study guide for Exam PL-300: https://learn.microsoft.com/en-us/credentials/certifications/resources/study-guides/pl-300 (opens in a new tab)
- Row-level security (RLS) with Power BI: https://learn.microsoft.com/en-us/fabric/security/service-admin-row-level-security (opens in a new tab)
- Row-level security guidance in Power BI Desktop: https://learn.microsoft.com/en-us/power-bi/guidance/rls-guidance (opens in a new tab)
- Roles in workspaces in Power BI: https://learn.microsoft.com/en-us/power-bi/collaborate-share/service-roles-new-workspaces (opens in a new tab)
- Semantic model permissions: https://learn.microsoft.com/en-us/power-bi/connect-data/service-datasets-permissions (opens in a new tab)
- Object-level security (OLS): https://learn.microsoft.com/en-us/fabric/security/service-admin-object-level-security (opens in a new tab)
- Sensitivity labels in Power BI: https://learn.microsoft.com/en-us/power-bi/enterprise/service-security-sensitivity-label-overview (opens in a new tab)
- Export data from a Power BI visual: https://learn.microsoft.com/en-us/power-bi/visuals/power-bi-visualization-export-data (opens in a new tab)
- Power BI implementation planning: Information protection: https://learn.microsoft.com/en-us/power-bi/guidance/powerbi-implementation-planning-info-protection (opens in a new tab)